
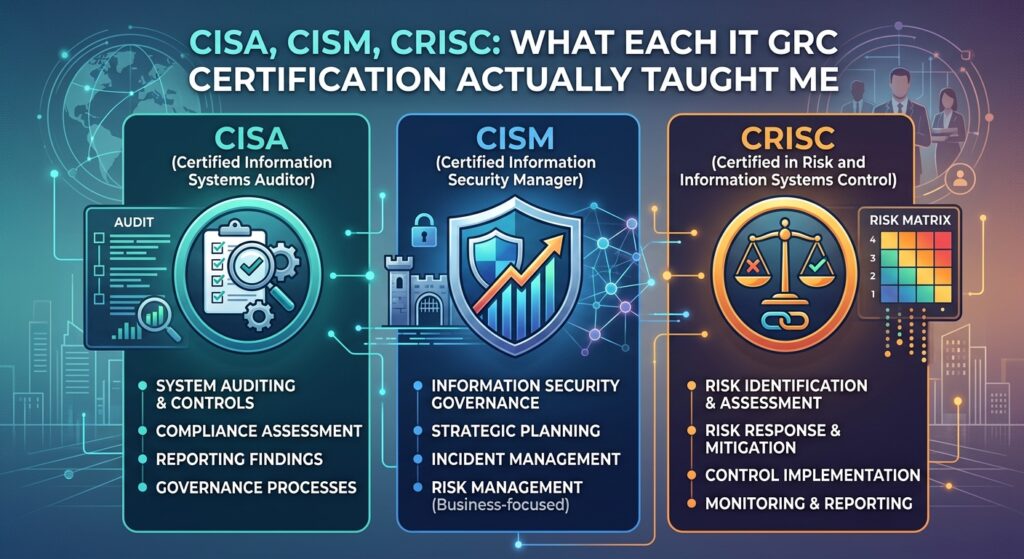
People often ask which IT GRC certification to take first. I usually tell them the sequence matters less than the mindset shift each one demands. I took mine in a specific order, CISA in 2022, CISM in 2023, CRISC in 2025, and each of these IT GRC certifications taught me something the others couldn’t.
CISA: The Hardest, Because Everything Was New
CISA had the steepest learning curve of the three. I was coming from an auditor’s seat at KPMG, where I’d spent years running IT General Controls and SOX assessments, and the CISA material still gave me genuinely new concepts in nearly every domain, especially around technology architecture and how it’s actually kept secure. Of the IT GRC certifications I hold, this is the one that felt least like a formality and most like real education.
But CISA also started a mindset shift I didn’t fully register until later: moving from an auditor’s instinct, where compliance is close to non-negotiable, toward something closer to a manager’s instinct, where you weigh what the business can actually prioritize.
CISM: Easier Material, Harder Mindset Shift
CISM overlapped heavily with what I’d already learned in CISA, so the material itself came easier. But of the three, this is the certification that stuck with me the most, not because of what was new, but because of what it undid.
Before CISM, I treated compliance as the upmost priority and control implementation as mostly non-negotiable. That was the instinct I carried through leading the ISO 27001, ISO 27701, and PCI-DSS certifications at TikTok Shop Indonesia. Studying governance properly, and forcing myself into a manager’s mindset rather than an auditor’s, changed how I saw that work. Compliance is not the finish line. It’s another risk to manage, like any other. Whether to implement a given control becomes a cost-benefit question, not a foregone conclusion.
That’s a small sentence to write and a real shift to internalize, especially coming from years of assurance work where a control either existed or it was a finding.
CRISC: Same Material, a Completely Different Universe
CRISC was tricky in a specific way. Much of the material overlapped with CISM. What was different was that neither the auditor mindset nor the manager mindset from the earlier two certifications transferred cleanly. CRISC asks you to think in terms of the full universe of risk being managed, not a specific control environment or governance program. That’s the lens I now carry into my DPO work at SPayLater, where a risk decision rarely stays contained to IT and has to be weighed against regulatory, operational, and reputational exposure all at once. It’s a wider aperture than either of the other IT GRC certifications required.
Who Each One Suits
If you’re deciding among these IT GRC certifications rather than reading about mine after the fact, the mindsets above translate fairly directly into who each one fits.
If you’re still sitting in an assurance or audit seat, CISA is the one that will teach you the most, because it forces depth in technology architecture and control design that audit work alone doesn’t always demand.
If you’re stepping into, or already holding, a security leadership seat where you’re accountable for tradeoffs rather than findings, CISM is the one that will actually change how you operate, since it’s the certification built around exactly that shift from enforcing controls to weighing them.
If your role sits at the intersection of multiple risk domains at once, IT, regulatory, operational, where a single decision has to account for all three simultaneously, CRISC is the one that gives you the framework for that, more than either of the other two.
None of this means you need all three to be credible in IT GRC. It means the value of each one depends on which seat you’re sitting in when you take it, which is also why I’d caution against choosing based on which certification looks best on paper rather than which mindset shift you actually need next.
Why This Order Worked for Me
I started as an auditor, then moved into assurance and GRC. CISA and CISM followed that trajectory naturally, each matching the seat I was sitting in at the time. CRISC came last and, in hindsight, encapsulated the other two well, pulling the auditor lens and the manager lens into a single risk-management view.
If you’re weighing these IT GRC certifications for yourself, I’d say the sequence matters less than matching it to your own transition, not someone else’s. No matter the order, each one gives real value and real new knowledge. The order just determines how naturally each one lands.
About Me
William Chandra is an IT GRC and data protection professional with years across Big 4 assurance, hypergrowth e-commerce, and OJK-licensed financial services. He holds CISA, CISM, CRISC, and ISO 27001:2022 Lead Auditor certifications and serves on the executive team of ISACA Indonesia’s Certification Office.
Connect with me on Linkedin.